


Cifas checks
Fraud prevention top of mind? Confidently make senior hires with Zinc’s Cifas Insider Threat Database (ITD) checks and protect your organisation from fraud, dishonest actions, and false employment applications.

Cross-check hires against a shared database of over 500 FCA-regulated members

Get a full picture of non-criminal misconduct

Prevent costly insider threats

What you need to know
Available in
United Kingdom
Cifas Insider Threat Database checks for UK member organisations


Identify fraud risk and protect your business from peer-reported bad actors.

Stop fraud in its tracks
Checking the Cifas Insider Threat Database (ITD) gives member organisations access to shared information to help prevent fraud, data exposure, or financial loss by employees. With an increase of 21% in entries from 2024 to 2025, you can’t afford to be out of the loop.

Build a solid audit trail
Insider fraud can be prevented with solid governance. Cifas checks help you keep a consistent audit trail, especially when used alongside identity verification, sanctions screening, and adverse financial checks.

Get member-reported data
Insider knowledge is invaluable. If common competitors or industry peers are Cifas members, they can report fraud risks, abuses of power, and misuse of data. This information is invaluable in building a safe, secure workforce.

See it in action
Book a demo and choose a time to speak with one of our experts about a custom solution for your business.

20
+

Integrated ATSs and HRISs
Instant
Results traight to your ATS
30
mins
Average time saved
Scan a members-only database straight from your Zinc account, and get results straight to your ATS or HRIS.
Get the inside scoop on insider threats
Instant results for faster hiring
UK government-approved
Results straight to your preferred HR platform



Total peace of mind.
“With Zinc handling our background checks, we have full confidence in the process. We know everything is being tracked, and we’ll be alerted right away if anything needs our attention.”

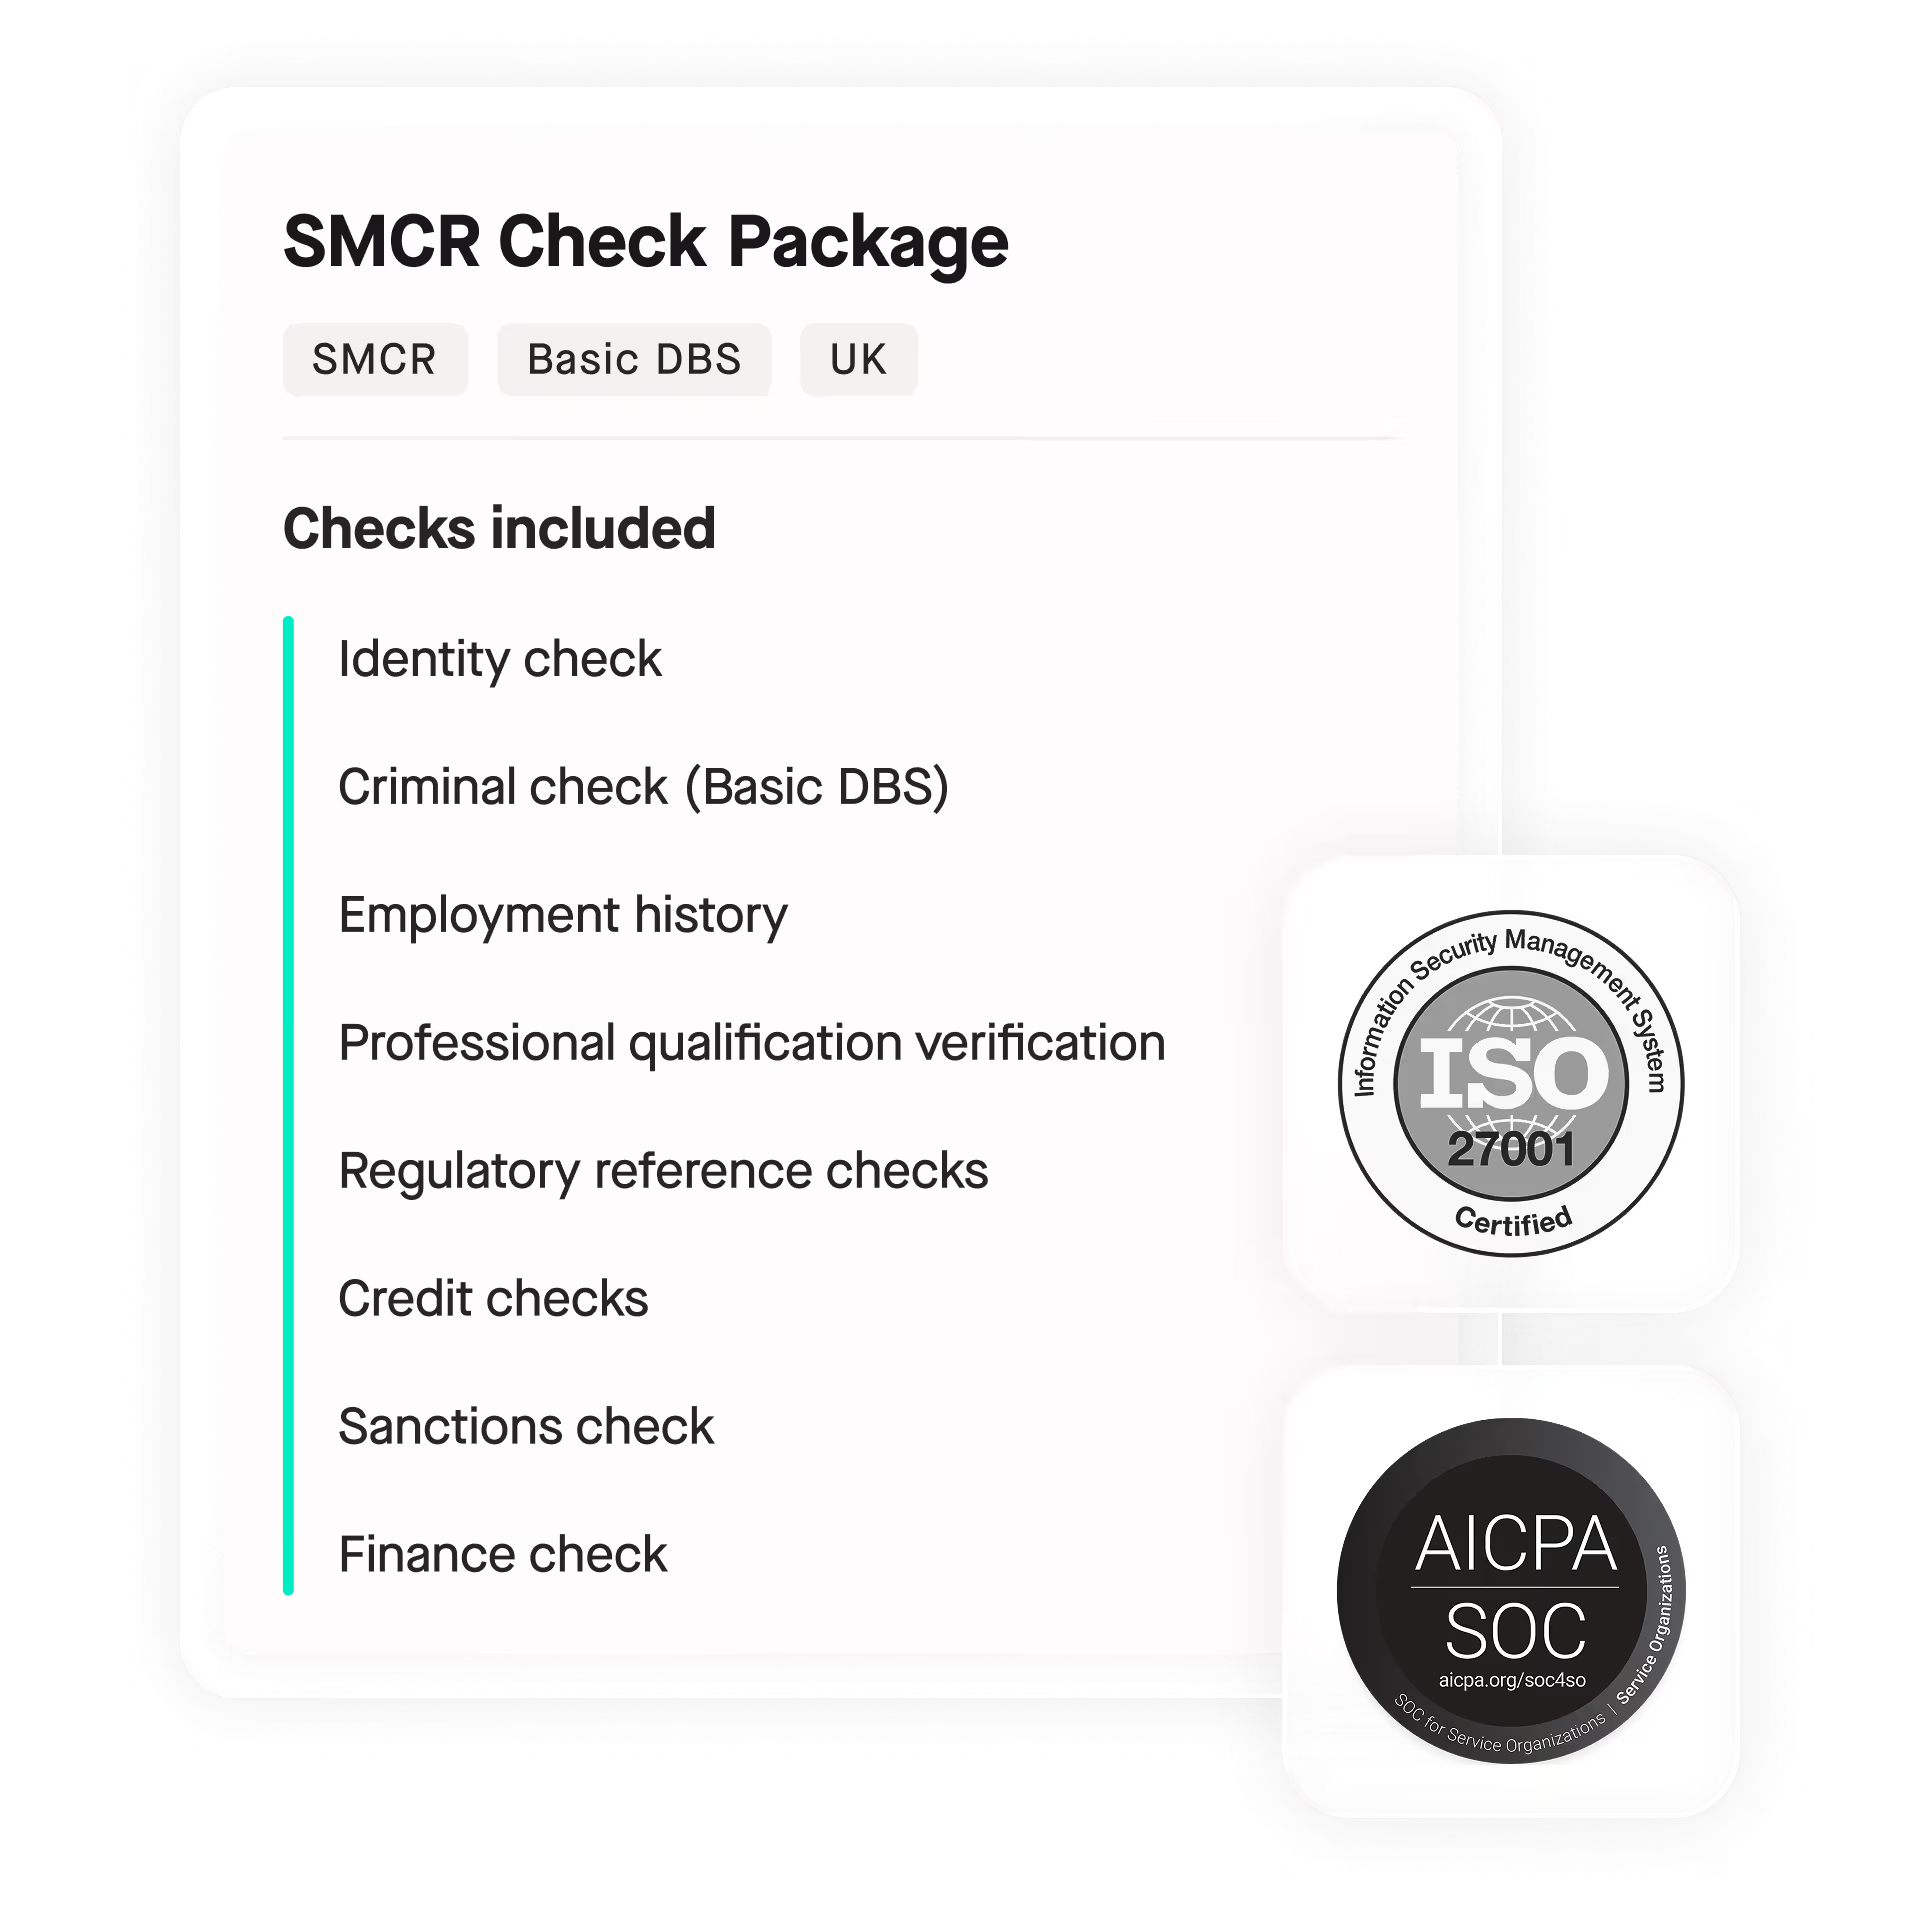
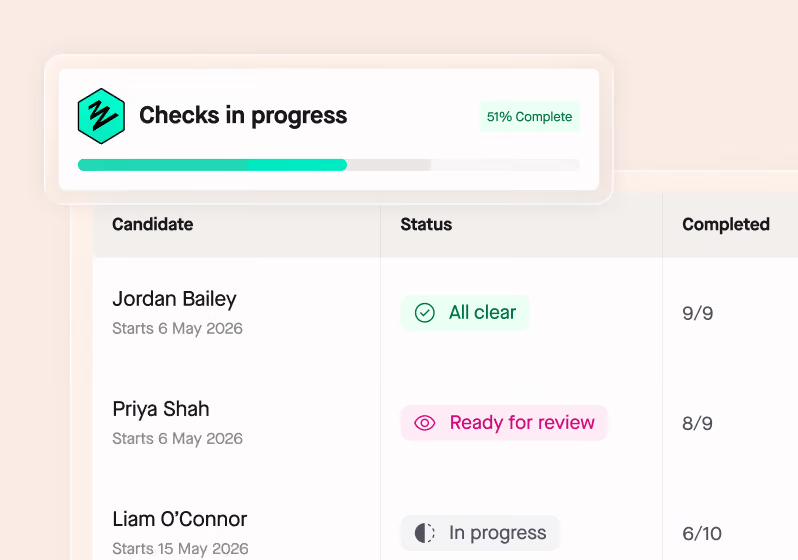
Scan the Cifas ITD directly from your Zinc dashboard and keep all your checks in one place.
Step one
To use Zinc’s Cifas checks, your organisation needs to be a registered Cifas member and have set up an integration with Zinc. Once that’s done, the check can be added to any screening package. As always, Zinc reuses identity and address data so you don’t need to do double data entry.
Step two
Zinc searches the Cifas Insider Threat Database (ITD), which holds records of confirmed fraud cases contributed by member organisations across financial services, insurance, and related sectors. It covers markers linked to abuse of position, false expense claims, data misuse, and dishonesty — the kind of behaviour that rarely makes it onto a criminal record.
Step three
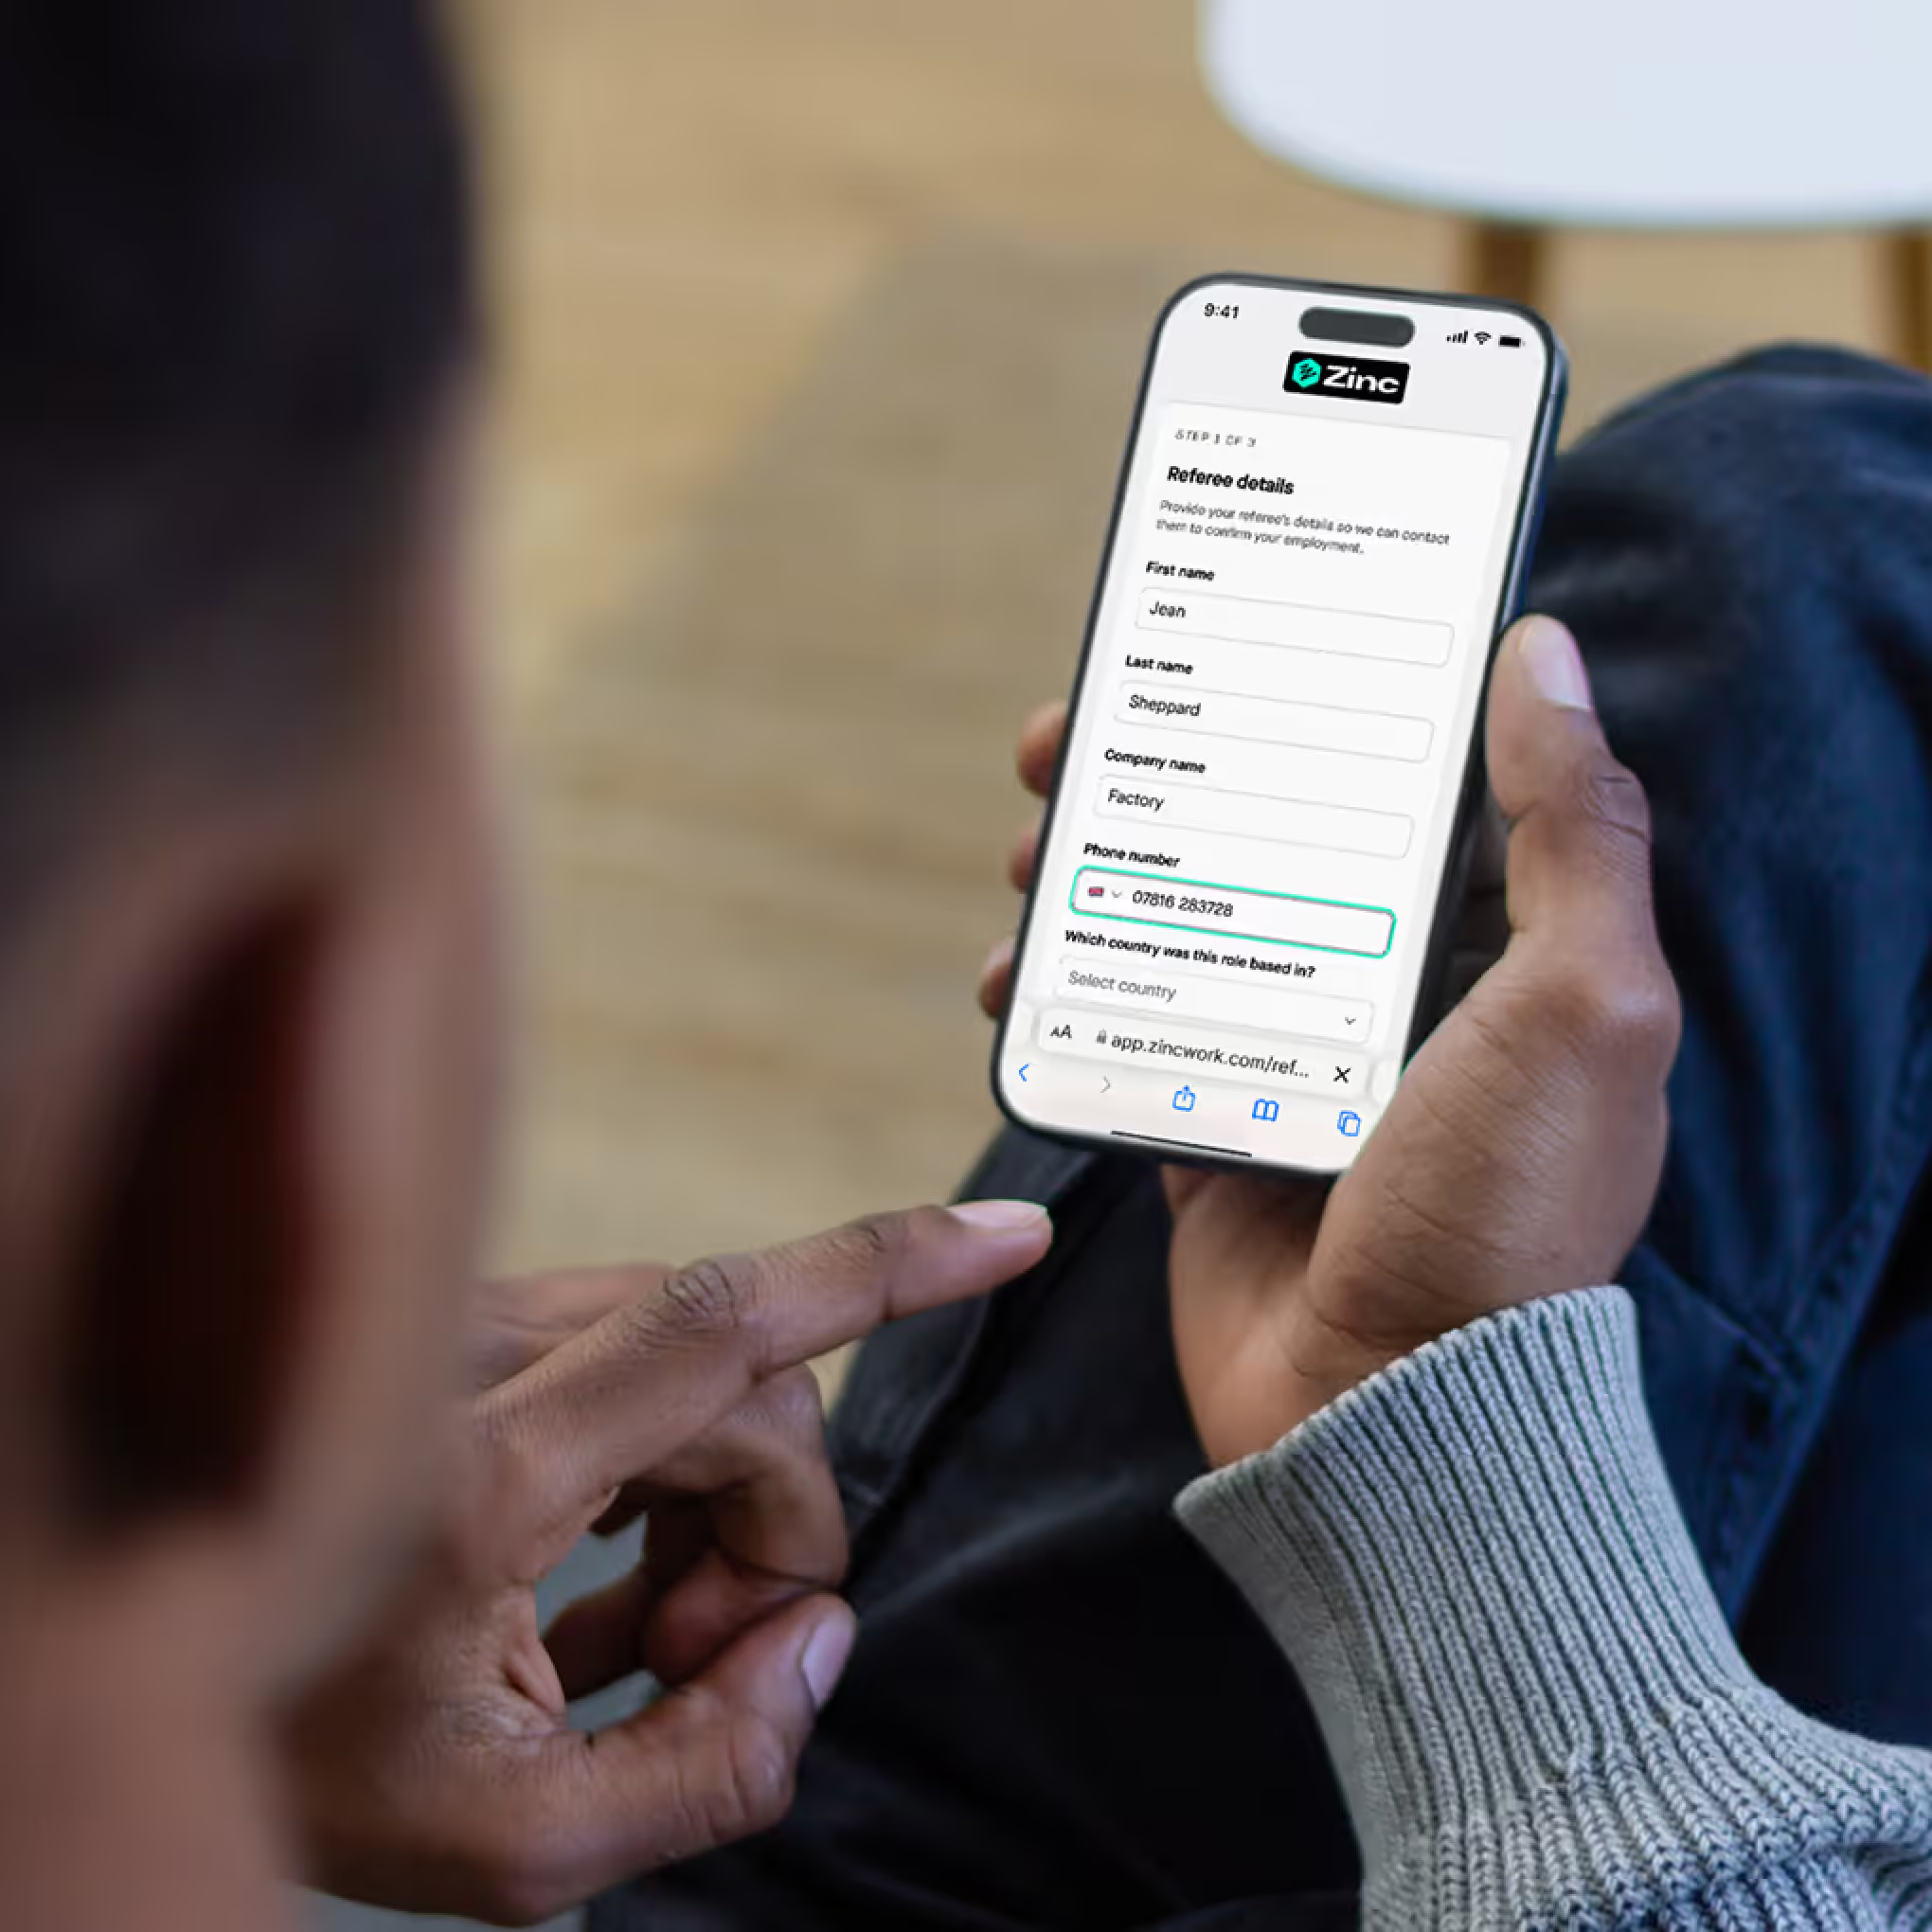
Results appear in your dashboard and feed into your ATS or HRIS workflow, saving around 30 minutes per candidate compared to manual Cifas checks.


Integrations
Background checks, integrated
Zinc connects directly with your ATS or HRIS at no additional cost. Send checks, get results, and store reports without leaving your preferred platform.
Why businesses love using Zinc


%%An intuitive, easy platform%% with support that's far quicker than other providers. The answers are always reliable, especially when we're dealing with different countries.
%%The candidate experience is excellent.%% Integration was straightforward, the pricing is among the best on the market, and support is quick and consistently helpful.
%%It automates the screening of new employees%% and integrates well with our ATS and HRIS. The initial setup was super easy and we're really happy with the product.
Onboarding takes just a few minutes and %%running checks for international contractors is seamless%%. The pay-per-use model is a huge plus for a small company like ours.
%%It has made my role, and my colleagues' day to day, much easier and more efficient%%, while significantly improving the overall experience for our candidates.
Checks and paperwork sync automatically with our recruitment and HR systems, %%saving us so much time%% not having to check multiple systems. The support teams are always incredibly helpful.
For teams of every size
Flexible background checks
Whether you’re hiring a little or a lot.

Under 20 hires annually
Pay As You Grow
Get started in minutes. Our Pay As You Grow plan is built for lower hiring volumes — a flat rate per check, with no hidden costs or setup fees.

Start checking in minutes, no setup needed
Flat rate per check, no hidden fees
Pay only for what you use
20+ hires annually
Custom solutions
For larger volumes, our experts build a package around your needs. Flexible with your hiring and never expires, with integrations, setup, training, and support all included free.
A custom package built around your hiring
Credit pool that never expires or rolls over
Integrations, setup, and training included free
More from Zinc
Check out more resources, straight from our experts



Start screening in days, not weeks
Combine this check with right to work, references, criminal records and more, across 195 countries, in a single candidate journey.
What is the Cifas Insider Threat Database and what does it detect for employers?
The Cifas Insider Threat Database (ITD) is a shared database maintained by Cifas, a UK fraud prevention charity and government-designated Specified Anti-Fraud Organisation.
It holds confirmed records of employees who abused their position of trust within an organisation. The categories of misconduct it covers include: financial abuse or theft, false expense claims, data theft or misuse, dishonest application for employment (providing false information to get a job), and other forms of dishonesty that breach the employment relationship. It also flags individuals who’ve been impersonated, which can be an early indicator of compromised identity or a wider fraud attempt.
The critical distinction from a criminal record check is that most insider fraud doesn't result in prosecution. Cases are typically resolved through employment law: the employee is dismissed, a settlement is reached, or the matter is handled civilly. The ITD captures these cases, contributed by Cifas member organisations predominantly in financial services, insurance, and related sectors.
Which organisations can run a Cifas Insider Threat Database check?
Access to the Cifas ITD is available only to registered Cifas member organisations. Membership is open to organisations across financial services, insurance, telecommunications, retail, and other sectors, and requires a formal application and an agreement to contribute data as well as use it.
If you're already a Cifas member, we’ll connect your membership to run ITD checks directly from your dashboard. If you're not yet a member but are considering it, our team can explain the process and benefits.
What happens when a candidate has a Cifas marker during employment screening?
A Cifas match means the candidate has been associated with a confirmed case of insider misconduct reported to the ITD by a member organisation. It's serious, but it isn't an automatic disqualifier.
Cifas’s own guidance, and good HR practice, is to assess matches on a case-by-case basis, taking into account the nature of the conduct, how long ago it occurred, and what the role involves. When a match appears in Zinc, it's flagged in your dashboard for review by your HR or compliance team. Review the details of the marker, assess its relevance to the role and the access the candidate would have, and document the decision-making process.
For FCA-regulated organisations, that documentation forms part of the fitness and propriety record. If the match raises material concerns, taking legal or compliance advice before proceeding is the right call.
What types of insider fraud does the Cifas Insider Threat Database cover?
The Cifas ITD covers confirmed cases in five main categories:
- Abuse of position (using access to systems, data, or relationships for personal gain)
- False expense claims (submitting dishonest expense reports or claiming payments not entitled to)
- Data theft or misuse (taking or misusing confidential company or customer data)
- Dishonest application for employment (providing false information on a job application to get the role)
- Other dishonest conduct that breaches the employment relationship
These are the categories most likely to cause significant financial or reputational damage and least likely to appear on a criminal record check, because most cases don't lead to prosecution. The ITD gives Cifas member organisations intelligence across sector boundaries that would otherwise be invisible.